A fresh account hack means obtaining or taking over a newly created gaming account that carries no ban history, no flags, and no suspicion from anti-cheat systems. Gamers pursue these accounts specifically to run cheats without triggering the detection systems tied to their main accounts. The appeal is straightforward: a clean slate lets you start over with full access to cheat software while the anti-cheat engine treats you like any other new player.
Here is what drives demand for fresh accounts among competitive gamers:
- Evading permanent bans on main accounts in games like EFT, Rust, and DayZ
- Running HWID spoofers and DMA cheat hardware without a flagged hardware profile
- Maintaining ranked progress on a secondary account while testing new cheat configs
- Accessing game regions or matchmaking brackets that a banned account cannot reach
- Reducing the risk of detection by pairing a fresh account with undetected cheat software
The risks cut both ways. Gamers who source these accounts carelessly expose themselves to malware, scams, and permanent data loss. Understanding how fresh account compromise actually works is the first step toward doing it safely, or avoiding it entirely.
Table of Contents
- How fresh account hacks actually work
- Early warning signs every gamer should recognize
- Risks of using hacked or unauthorized gaming accounts
- Safe, undetected cheat software and hardware options
- How Midnight-market keeps your account and hardware safe
- How to identify trustworthy sources for fresh accounts and cheats
- How fresh account hacks affect game communities and developers
- Guidelines for playing responsibly without hacks
- Midnight-market gives you the edge without the risk
- Key Takeaways
How fresh account hacks actually work
Most fresh account compromises do not involve brute-force password cracking. Modern attackers abuse legitimate authentication workflows instead, which makes the attack nearly invisible to standard defenses.
- Passkey enrollment hijacking: Threat group O-UNC-066 weaponizes Microsoft's own passkey enrollment process. An attacker calls the target, poses as IT support, and walks them through enrolling a passkey that actually belongs to the attacker. Once registered, that key grants persistent, MFA-resistant access.
- ClickFix and ConsentFix: These techniques steal valid session tokens without ever touching a password or MFA code. The victim pastes a device code into a dialog the attacker controls, handing over a live session in roughly three seconds.
- OAuth permission abuse: Attackers trick users into granting broad permissions to fake apps. Those OAuth grants survive password resets because they operate at the mailbox level, below the authentication layer.
- Phishing replicas: Pixel-perfect fake login alerts mimic real platform notifications, directing users to credential-harvesting pages.
- Social engineering via phone (vishing): Attackers use real-time operator-controlled phishing panels rather than automated proxy kits, allowing them to adapt the script live.
"Phishing attacks that do not steal passwords but hijack valid sessions represent a new challenge that demands structural and policy defenses beyond user training." — Secure in Seconds
The core problem is that these methods abuse legitimate platform features. There is nothing to patch. The attack looks like normal user behavior because, technically, it is.
Early warning signs every gamer should recognize
Catching a fresh account compromise early is the difference between a recoverable situation and a permanent loss. Adaptive Security flags these as the most reliable early indicators:
- Unsolicited MFA prompts arriving on your phone when you are not logging in
- Sudden login failures despite using the correct password
- Emails in your sent folder you did not write
- Password reset notifications you never requested
- Forwarding rules or OAuth app grants you did not set up
- Login history showing unfamiliar IP addresses or impossible geographic locations
- Recovery email or phone number changed without your action
That last one is the critical turning point. Once an attacker changes your recovery methods, standard self-service recovery stops working. What started as a temporary intrusion becomes a full takeover, leaving the legitimate account owner locked out permanently.
Pro Tip: Check your account's active sessions and OAuth app permissions at least once a month. Malicious forwarding rules and rogue app grants persist after a password reset, so a password change alone does not clean a compromised account.
Risks of using hacked or unauthorized gaming accounts
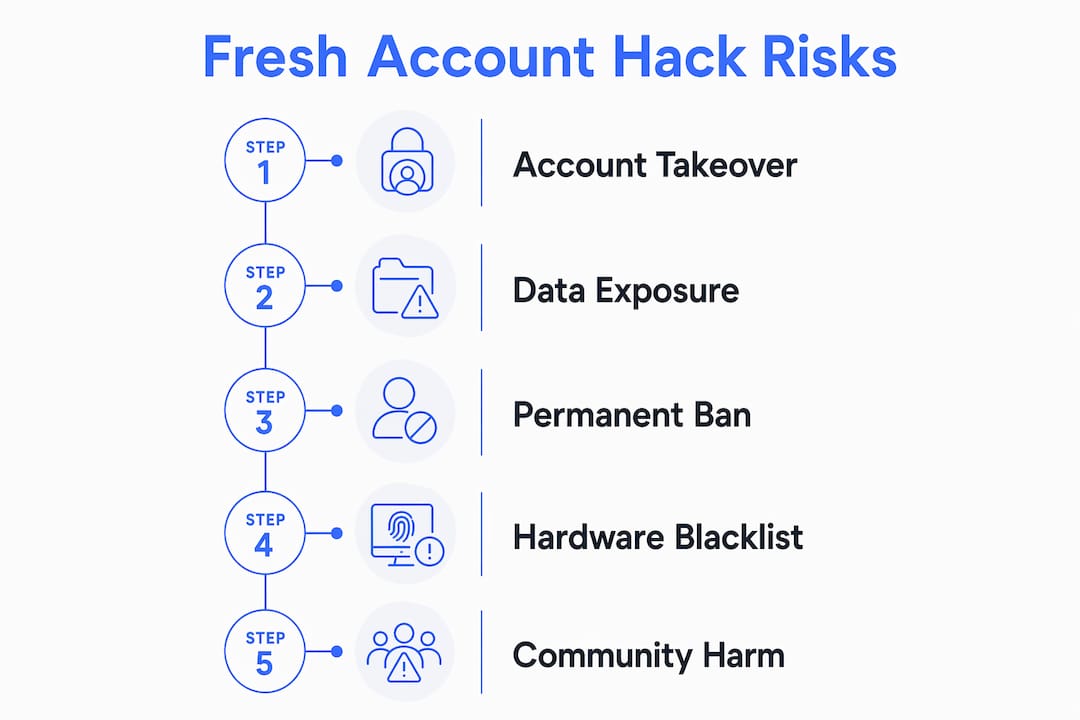
The consequences of sourcing accounts carelessly go well beyond a ban. They can be permanent and financially painful.
- Irreversible account deletion: Microsoft permanently deleted a hacked Xbox account that had been active for 25 years, including all OneDrive files and purchased games, with no restoration path offered.
- Loss of purchases: Digital game libraries, in-game items, and years of progression can vanish with the account.
- Malware exposure: Accounts sold through unverified channels often come bundled with credential-stealing software.
- Scams and false promises: Sellers frequently take payment and deliver nothing, or deliver accounts that get banned within hours.
- Community and developer crackdowns: Anti-cheat teams actively track fresh account patterns. A wave of new accounts running identical cheat signatures gets flagged fast.
- Legal exposure: Unauthorized account access violates platform terms of service and, in many jurisdictions, computer fraud statutes.
The Microsoft case is worth sitting with. The account's encryption architecture meant that even Microsoft's own engineers could not retrieve the deleted files. Sourcing a hacked account from an unreliable seller puts you one ban wave away from that same outcome.
Safe, undetected cheat software and hardware options
The alternative to sourcing compromised accounts is using purpose-built cheat software and hardware that is designed from the ground up to stay undetected. Midnight-market offers a catalog of tested solutions across the most popular titles:
- Nextcheat DayZ Cheats: Aimbot, ESP, and radar features built specifically for DayZ, with daily testing to confirm undetected status.
- NightFall Rust DMA Cheats: DMA-based hardware cheats for Rust that operate outside the game process, making them significantly harder for anti-cheat software to detect.
- Reported Temp Spoofer and HWID spoofers: Hardware ID spoofers that mask your physical machine's fingerprint, letting a fresh account stay clean even on a previously flagged system.
- Sensory Valorant DMA Cheats: Aimbot, ESP, and radar for Valorant, maintained with active detection monitoring.
- DMA hardware cards: Physical cards that run cheat software on a separate device, keeping the cheat process entirely invisible to the game client.
Every product on Midnight-market comes with a warranty on hardware items and a daily testing guarantee. Live Discord support means you get real-time help during setup, not a ticket queue that responds three days later.
Pro Tip: Pair a HWID spoofer with any fresh account before running cheat software. Anti-cheat systems like BattlEye and Easy Anti-Cheat flag hardware signatures, not just accounts. Spoofing the hardware ID breaks that link.
How Midnight-market keeps your account and hardware safe
Midnight-market's safety model rests on three concrete practices rather than marketing claims.
- Daily testing: Every cheat product is tested each day against the current anti-cheat build. If a product goes detected, it gets pulled until it is clean again.
- Live Discord support: Real-time assistance during installation and troubleshooting, available directly through Discord. No waiting, no generic FAQ responses.
- Hardware warranties: Physical DMA cards and spoofers come with warranties, which is rare in this market and signals genuine confidence in the product quality.
- Instant delivery: Products are delivered immediately after purchase, reducing the window between payment and setup where things can go wrong.
"Users benefit from immediate help and prompt access to products, reducing downtime and risk during cheat implementation." — Midnight-market
The undetected cheats catalog covers EFT, Valorant, Rust, DayZ, Apex Legends, and more. The combination of daily testing and live support is what separates a reliable provider from one that disappears after your payment clears.
How to identify trustworthy sources for fresh accounts and cheats
Not every seller claiming to offer fresh accounts or undetected cheats delivers what they promise. A few concrete filters cut through the noise:
- Active community presence: Legitimate providers maintain public Discord servers with real user activity, not ghost channels with pinned messages and no conversation.
- Verifiable testing schedules: Trustworthy cheat providers publish their testing status publicly and update it daily. If a provider cannot tell you when a product was last tested, that is your answer.
- Hardware warranties: Any provider selling DMA hardware without a warranty is telling you something about how much they trust their own product.
- Transparent refund and ban policies: Clear policies on what happens if a product goes detected mid-subscription signal accountability.
- No upfront payment to anonymous sellers: Fresh accounts sold through Discord DMs with no storefront, no reviews, and no recourse are almost always scams or malware delivery vehicles.
How fresh account hacks affect game communities and developers
Fresh account hacking and cheat use do not exist in a vacuum. The effects ripple outward in ways that shape how developers build their anti-cheat systems and how legitimate players experience the game.
Developers respond to cheat waves by tightening account creation restrictions, adding phone verification requirements, and deploying kernel-level anti-cheat drivers. Each escalation raises the bar for everyone, including players who have never touched a cheat. Legitimate new players get caught in false-positive ban waves when their hardware profile resembles a flagged pattern.
For the broader community, widespread cheating in ranked modes erodes trust in the matchmaking system. Player retention drops when losses feel illegitimate. Developers then face pressure to invest in anti-cheat infrastructure rather than content, which slows the game's development cycle.
Guidelines for playing responsibly without hacks
Competitive gaming without cheats is still winnable at high levels, and it carries none of the account risk.
- Use legitimate aim trainers like Aim Lab or KovaaK's to build mechanical skill that transfers across titles.
- Review your own gameplay footage. Most rank ceilings come from decision-making errors, not mechanical limits.
- Keep your accounts secured with two-factor authentication and unique passwords per platform.
- Back up any digital purchases or account data you cannot afford to lose, since the Microsoft Xbox case shows that even platform providers cannot always recover deleted content.
- If you do use cheat software, source it from providers with verifiable daily testing and real support, not anonymous Discord sellers.
Midnight-market gives you the edge without the risk
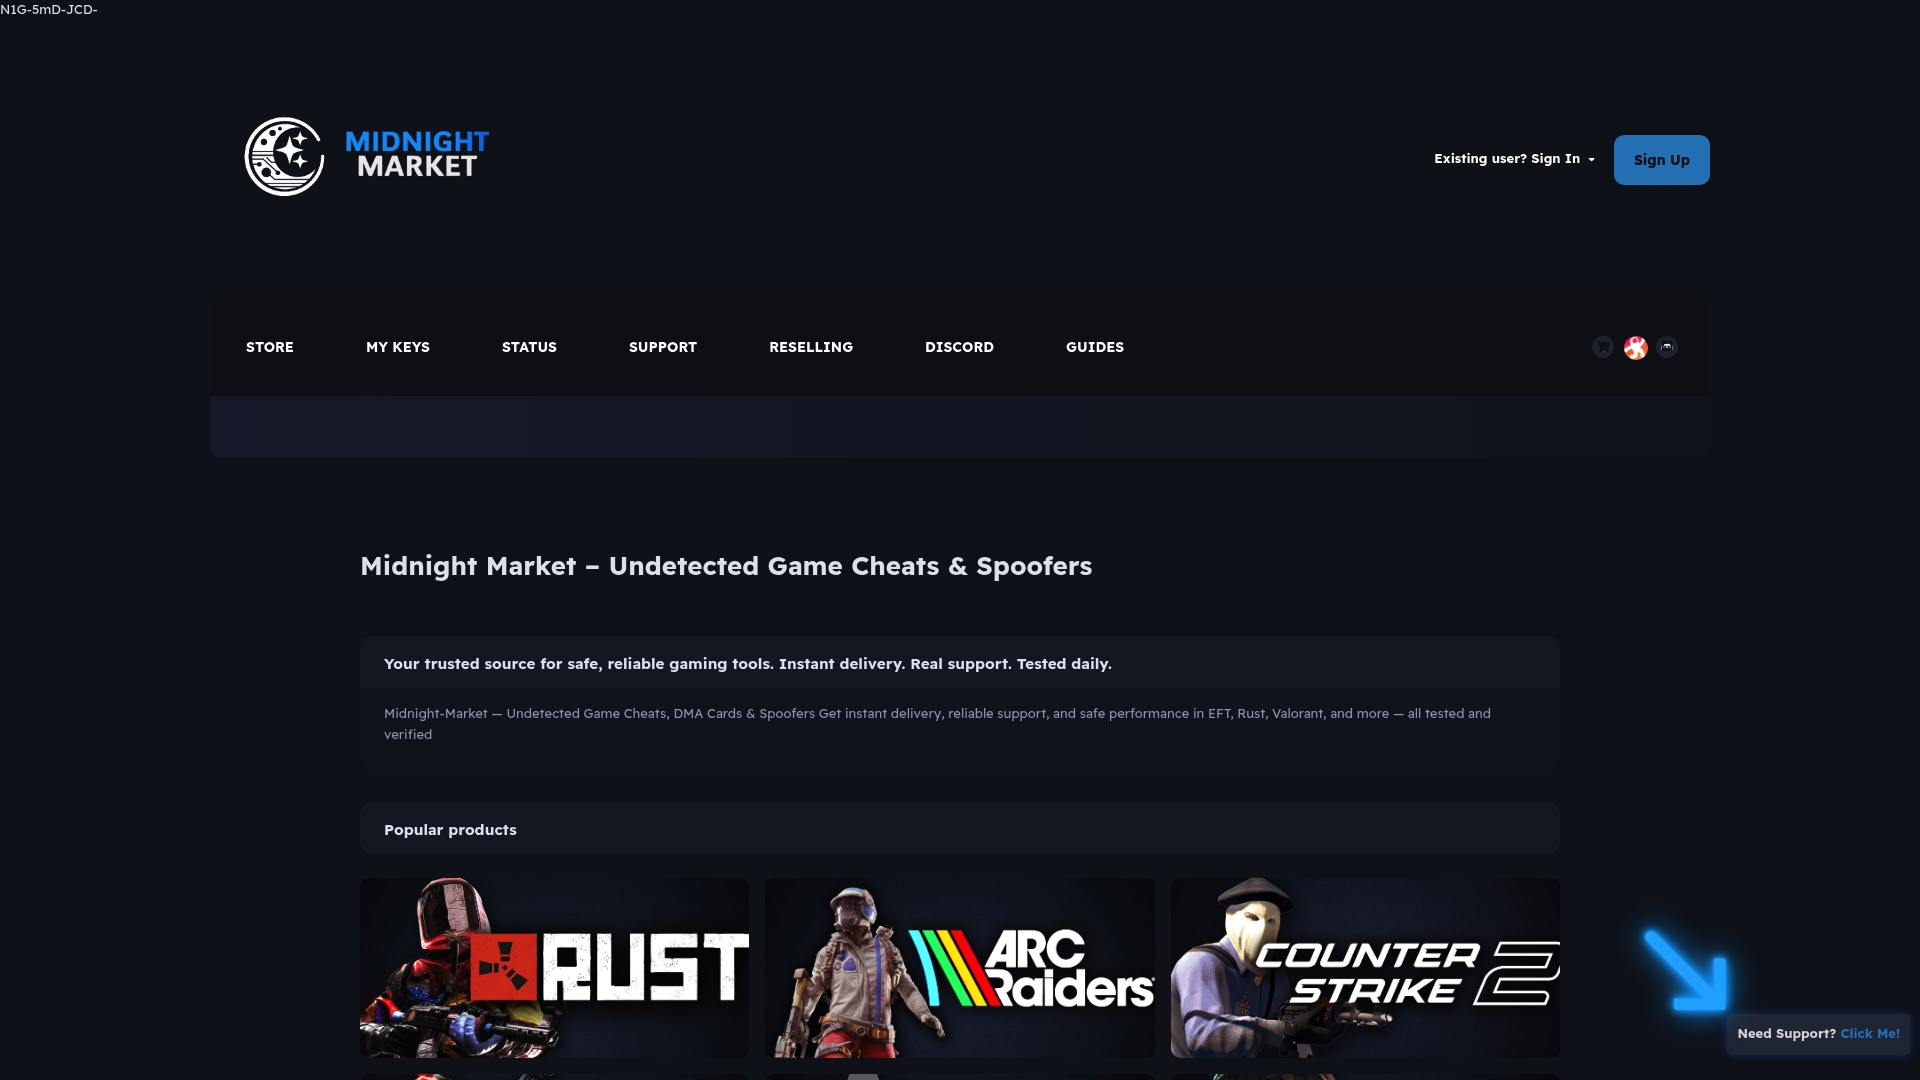
Sourcing random fresh accounts from unverified sellers is a gamble with your hardware, your money, and your data. Midnight-market is built for gamers who want a real competitive advantage without the exposure that comes with sketchy account markets. Every product in the Midnight-market store is tested daily, delivered instantly, and backed by live Discord support. Hardware products carry warranties. If something goes detected, you hear about it before you log in, not after a ban.
The catalog covers the titles where detection risk is highest: EFT, Valorant, Rust, DayZ, Apex Legends, and more. Whether you need a Nextcheat DayZ setup or a full DMA hardware configuration, the products are maintained by people who treat detection avoidance as an ongoing technical problem, not a one-time setup. Check the store, pick your title, and get set up with support that actually responds.
Key Takeaways
Fresh account hacks carry serious permanent risks, and the safest path to undetected competitive play is purpose-built cheat software with daily testing and hardware spoofing.
| Point | Details |
|---|---|
| Fresh account compromise is permanent | Microsoft permanently deleted a hacked Xbox account with no restoration path for purchases or files. |
| Attacks bypass MFA without cracking it | ClickFix and ConsentFix steal live session tokens in seconds, with no password or MFA code needed. |
| HWID spoofing is essential | Anti-cheat systems flag hardware signatures, so a fresh account alone does not protect a previously banned machine. |
| Warning signs demand immediate action | Unsolicited MFA prompts and sudden login failures signal an active cyberattacker is inside or targeting the account, giving you only a narrow window to act before permanent takeover. |
| Midnight-market provides daily-tested solutions | Products like NightFall Rust DMA Cheats and Nextcheat DayZ Cheats are tested daily and backed by live Discord support and hardware warranties. |