A clean hack is an undetected cheat setup: a combination of HWID spoofer, DMA hardware, or vetted cheat software configured so anti-cheat sees no local artifacts. The fastest path to a working low-detection setup is a vendor-tested bundle from Midnight-market that pairs cheat software with an HWID spoofer and optional DMA hardware, delivered instantly with live Discord support and a hardware warranty.
A complete clean-hack bundle needs all of these:
- Cheat software tested daily against the target game's anti-cheat build
- HWID spoofer that randomizes all major hardware identifiers atomically
- DMA hardware (optional but highest stealth) for off-host memory processing
- Live support for setup questions and post-update troubleshooting
- Hardware warranty covering firmware corruption or device failure
Table of Contents
- What you'll find in this guide
- How does DMA bypass kernel anti-cheat?
- What is the exact preflight order to minimize detection?
- What are the real risks and how do you manage them?
- Which Midnight-market bundles are worth buying?
- Key Takeaways
- The part most buyers get wrong
- Get a vetted clean-hack bundle from Midnight-market
What you'll find in this guide
This article walks you through every layer of a working undetected setup:
- A technical primer on how DMA bypasses kernel anti-cheat
- A catalog of every HWID vector modern spoofers cover
- An exact preflight checklist with the correct order of operations
- Current anti-cheat defenses and their realistic limits
- Risk controls and account-hygiene practices
- Recommended Midnight-market bundles with product details
- A purchase CTA with instant delivery and support info
After reading, you'll be able to choose the right bundle, run preflight correctly, and install safely. Product links and live Discord support are available directly through Midnight-market's store.
How does DMA bypass kernel anti-cheat?
DMA devices read game memory directly from the PCIe bus without executing any code on the gaming PC. Kernel anti-cheat scans for injected DLLs, suspicious processes, and unauthorized syscalls. None of those exist on the gaming PC when DMA is in play, because all the cheat logic runs on a second machine.
The standard architecture: an FPGA-based PCIe card sits in the gaming PC's PCIe slot and reads RAM. That data streams to a second PC running memory-extraction software like PCILeech, which processes game state and renders overlays entirely off-host. The gaming PC never executes cheat code.
Why kernel anti-cheat struggles:
- No injected DLLs or in-process hooks to scan
- No local cheat process visible in Task Manager or kernel callbacks
- No syscall traces from unauthorized drivers
- Hardware-level reads that bypass OS-layer monitoring entirely
The remaining attack surface is the DMA device itself. Anti-cheat can query PCIe configuration space and check device identifiers. Premium DMA firmware counters this by spoofing Vendor/Device IDs, emulating BAR layouts, and mimicking the full configuration space of common peripherals like network cards. IOMMU complicates this further: it maps which PCIe devices can access which memory regions, and a device that reads outside its assigned range can trigger a fault. Security research has cataloged PCIe-layer bypass techniques and the defensive options defenders have at the bus level, including hypervisor-level controls that go beyond what most consumer anti-cheat currently enforces.
What is the exact preflight order to minimize detection?
Follow this sequence every session. Skipping or reordering steps is the most common cause of detection.
- Cold reboot the gaming PC with no cheat software loaded
- Open Task Manager → Services and confirm no anti-cheat service (Vanguard, EAC, BE) is running
- Disable auto-launch entries for any game client that starts anti-cheat at login (use
msconfigor Task Scheduler) - Map the HWID spoofer using the vendor's loader — do not open the game first
- Verify spoofed IDs using a hardware-info tool to confirm all vectors changed
- Check BIOS settings: IOMMU should be enabled for DMA setups; Secure Boot state depends on your spoofer's kernel signing requirements
- Connect DMA hardware via PCIe or Thunderbolt; confirm the second PC sees the device before launching the game
- Start the game only after all spoof and DMA verification steps pass
- Test in a non-ranked lobby before entering competitive play
Pro Tip: Back up your original hardware IDs before the first spoof session using a tool like HWiNFO64. Store that snapshot offline. If you ever need to restore a clean state for RMA or warranty service, you'll have the exact original strings.
For DMA overlays, calibrate screen position on the second PC before entering a match. Miscalibrated overlays that lag or misalign are a behavioral signal even when the cheat itself is undetected. The Midnight-market hardware setup guide covers port handling and overlay calibration in detail.
What are the real risks and how do you manage them?
Account bans and hardware forensics are the two primary consequences. Managing them requires layered controls, not a single silver bullet.
Forensic traces that can appear even with a working spoofer:
- PCIe device telemetry logged server-side during a session
- Firmware mismatches between spoofed IDs and behavioral device signatures
- Unusual gameplay telemetry (perfect tracking, zero reaction variance)
- Linked accounts sharing payment methods, emails, or IP ranges
| Risk level | Scenario | Recommended action |
|---|---|---|
| Low | Software cheat, no spoofer, casual title | HWID spoofer minimum; ephemeral spoof per session |
| Medium | Software cheat + spoofer, ranked play | Firmware-level spoof; practice account first |
| High | DMA hardware, top-tier anti-cheat (Vanguard, BE) | Full DMA bundle + firmware spoof + hardware warranty |
Account hygiene checklist for maintaining a clean account:
- Use a separate email and payment method for any account tied to cheating
- Never mix personal accounts and spoofed-hardware sessions on the same machine
- Keep original ID backups and a rollback procedure ready
- Stage testing on a secondary account before using on your main
- Avoid streaming or screen-sharing during sessions
Which Midnight-market bundles are worth buying?
Midnight-market bundles are the recommended route because every product is tested daily against the target game's live anti-cheat build, delivered via instant key, and backed by live Discord support and a hardware warranty. That combination of daily testing, real-time help, and warranty coverage is what separates a vetted provider from a forum reseller.
Valorant DMA bundles:
- Evo Valorant DMA Cheats: aimbot, ESP, and radar on a DMA architecture. Stealth level: high. Delivery: instant key. Warranty: hardware covered.
- Sensory Valorant DMA Cheats: alternate Valorant DMA option with different feature weighting and support tier. Good for players who want a different configuration profile.
Hardware:
- Godlike 10th Gen Fuser: firmware-level DMA fuser hardware for buyers who want persistence across sessions without reconfiguring each time.
Anti-cheat-specific bundles:
- BE Elite Bundle: BattlEye-compatible bundle covering titles like Rust and DayZ.
- Nextcheat ARK Ascended Cheats: aimbot, ESP, and god mode for ARK Ascended.
Buyer questions to ask before any purchase: Which games are supported? How often are detection logs updated? What is the rollback procedure if an update breaks compatibility? What does the hardware warranty cover and for how long? Is delivery instant or does hardware ship separately?
Midnight-market's DMA cheating guide publishes setup walkthroughs and preflight checklists aligned with what's covered here.
Key Takeaways
A clean hack requires three layers working together: a daily-tested cheat, an atomic HWID spoofer covering all major vectors, and correct preflight order every session.
| Point | Details |
|---|---|
| Definition | A clean hack combines undetected cheat software, an HWID spoofer, and optional DMA hardware so anti-cheat finds no local artifacts. |
| Preflight order | Reboot clean, confirm no anti-cheat services running, apply spoof, verify IDs, then start the game. Never reverse this sequence. |
| Biggest detection risk | Firmware mismatches and behavioral telemetry; firmware must stay current after every anti-cheat vendor update. |
| Account hygiene | Use separate email and payment, keep original ID backups, and test on a secondary account before your main. |
| Midnight-market | Daily-tested bundles with instant key delivery, live Discord support, and hardware warranty cover Valorant, ARK, Rust, and more. |
The part most buyers get wrong
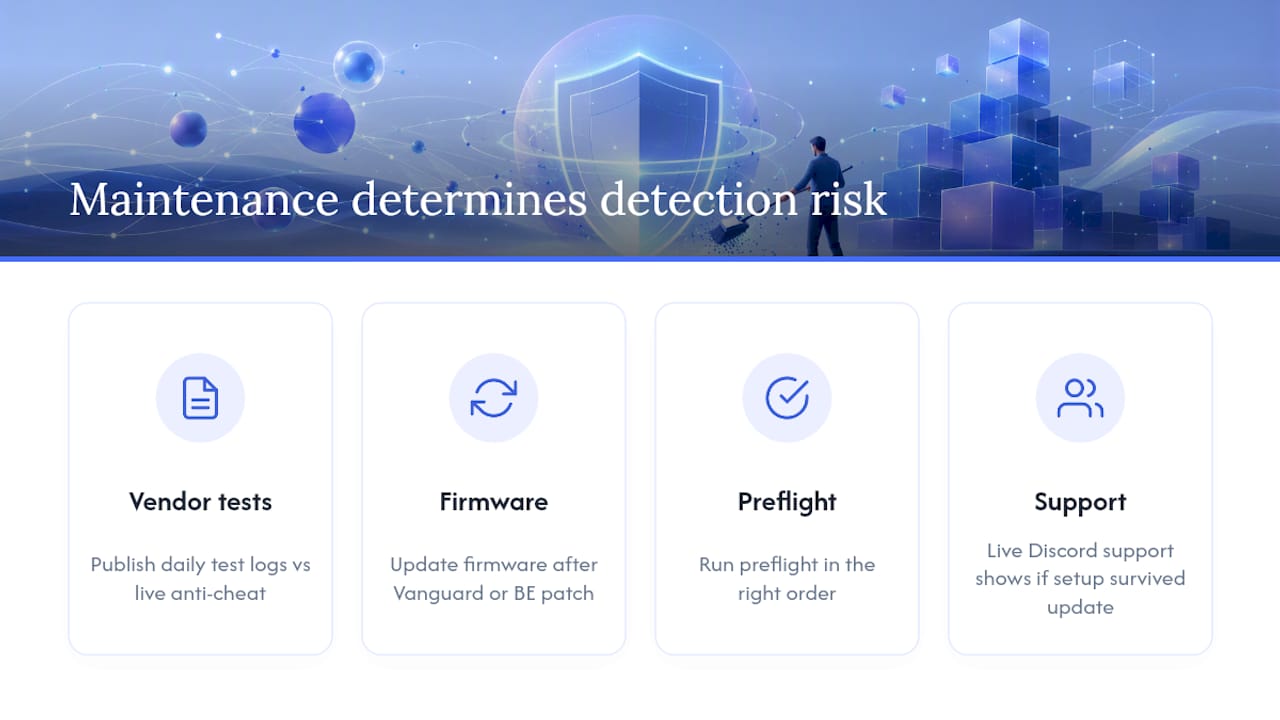
Most players shopping for a clean hack focus entirely on the cheat feature list: aimbot range, ESP draw distance, radar accuracy. Those matter, but they're not what gets you banned or keeps you safe. What actually determines your detection risk is the maintenance layer: how often the vendor tests against the live anti-cheat build, whether the firmware gets updated after a Vanguard or BE patch, and whether you ran preflight in the right order.
The Vanguard IOMMU enforcement event is the clearest example. Players with expensive DMA hardware got their FPGA firmware corrupted not because the cheat was detected mid-session, but because they hadn't updated firmware before launching a patched version of Vanguard. The cheat itself was fine. The maintenance gap was the problem.
Vendors who publish daily test logs and offer live Discord support aren't just marketing. They're the only realistic way to know whether your setup survived last night's anti-cheat update before you queue into a ranked match.
Get a vetted clean-hack bundle from Midnight-market
Midnight-market delivers what most forum resellers can't: daily-tested cheat software, atomic HWID spoofers, and DMA hardware bundles with a real hardware warranty and live Discord support standing by for setup questions.
Browse the full catalog at the Midnight-market store, where you'll find Valorant DMA bundles, BattlEye and EAC-specific packages, standalone HWID spoofers, and the Godlike 10th Gen Fuser for firmware-level persistence. Digital keys deliver instantly at checkout. Hardware ships separately with warranty documentation included. For setup help or post-update troubleshooting, the Discord support team responds in real time. Start with the bundle that matches your game and anti-cheat target, run the preflight checklist in this guide, and you're operational the same day.